
01 / ASSESS
Penetration testing
Find exploitable weaknesses across applications, APIs, and infrastructure. Work through evidence and remediation with your team.
Explore this service ↗OFFENSIVE SECURITY & TRAINING
Find the weaknesses an attacker could exploit. Give your team the skills to find and fix them.
IN THEIR WORDS
Selected lesson reviews and recommendations from Superprof.
“I came out becoming more confident about my upcoming interview.”
“the way of his teaching is awesome, he will go step by step”
“It's an awesome experience to get knowledge by Mr. Muzkkir !”
“Muzkkir is smart, organized, and conscientious.”
“He's been my friend and mentor since then.”
“Well organized, helpful materials, great structure of the course.”
“he was very patient and explained all the concepts very clearly.”
“smart and structured straight to the point nice person would hire again”
“Muzkkir makes sure you understand everything you are doing and guides you through every step!”
02 / ABOUT ZSECURES
Zsecures grew from a Canadian initiative to help people connect academic knowledge with practical cybersecurity work. Led by Muzkkir, it brings together teaching, testing, research, and building tools.
Get to know usNEW ON UDEMY / AI SECURITY
Work through Python models, prompt injection, agent risks, and defenses in Muzkkir’s self-paced AI red teaming course.

01 / SERVICES
From the first test to the next fix, know what to focus on and why it matters.
01 / ASSESS
Find exploitable weaknesses across applications, APIs, and infrastructure. Work through evidence and remediation with your team.
Explore this service ↗02 / LEARN
Build practical skills, prepare for an exam, or work through a focused topic with a mentor.
Explore this service ↗03 / PLAN
Understand your findings, prioritize changes, and plan the next stage of your security work.
Explore this service ↗04 / EXPLORE
Read the field notes, explore the tools, and register for updates from Muzkkir and Zsecures.
Explore this service ↗INSIDE AN ASSESSMENT
A single endpoint rarely tells the whole story. Look at how identity, permissions, and application behavior connect.
Explore penetration testing ↗CHOOSE YOUR FORMAT
Focused sessions with time to revisit a topic and ask the questions that matter to you.
Practice technical reasoning and explaining your approach clearly.
Discuss exercises and prerequisites around the technologies your team uses.
Work through realistic scenarios in an environment designed for learning.
Testing starts with explicit authorization and an agreed scope. Discuss production constraints, data handling, and who to contact if something needs attention.
For teaching, use labs and systems you have permission to test. Understanding those boundaries is part of the skill.
FROM MUZKKIR’S BLOG
Go deeper into the technical work through write-ups, walkthroughs, and reference notes.
Read how a weakness works and follow the reasoning behind an investigation.
Explore CTF scenarios and the steps used to solve them.
Keep practical commands and techniques close while you work.
THE WORK SO FAR
Across Muzkkir’s teaching, projects, and security work. Figures supplied by the founder; tools and labs are approximate.
BUILT AROUND YOUR ENVIRONMENT
A focused automation script. A secure application. A lab that teaches a specific scenario. Start with the problem and we’ll work out what a useful first version should do.
Custom tools & solutions ↗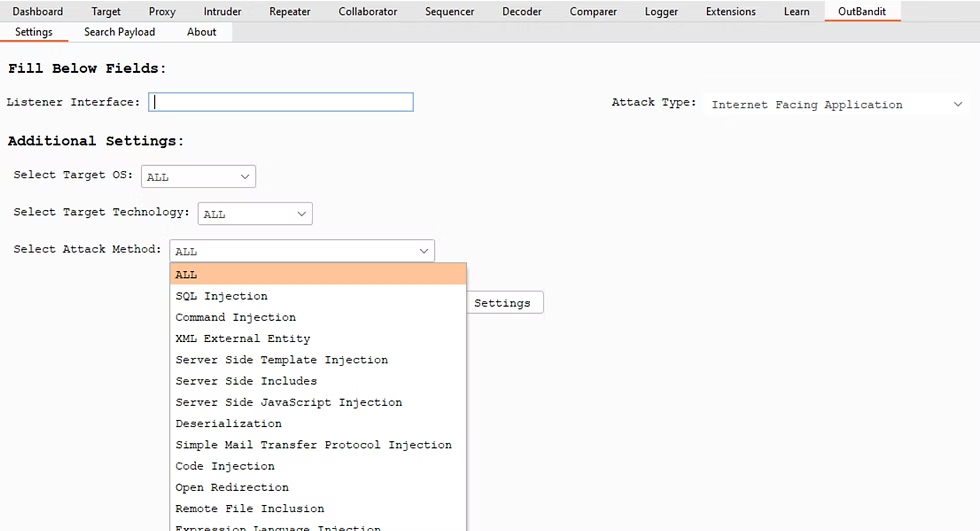
FROM THE LAB
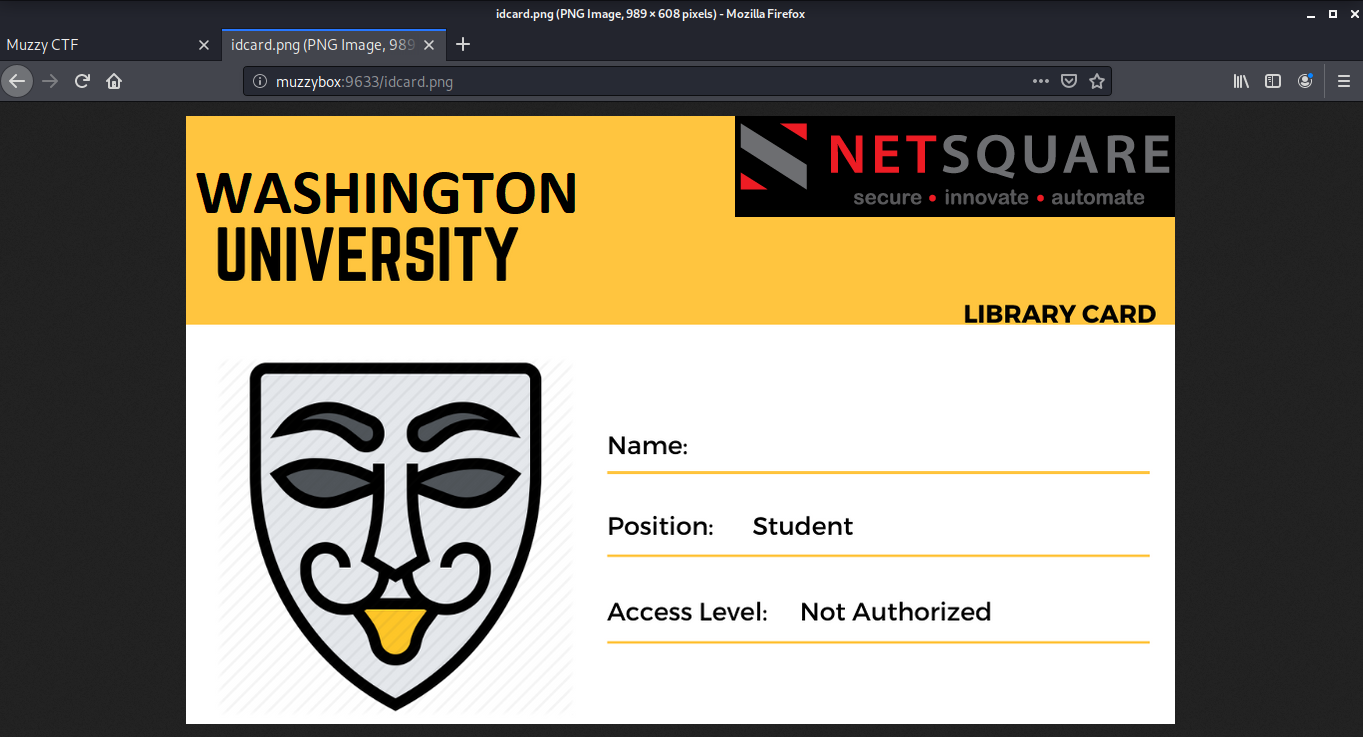
Explore MuzzyBox and FinitHicDeo, two labs from Muzkkir’s project portfolio. Follow the clues, test your reasoning, and read the source when you want to go deeper.
Explore the labs and repositories ↗LEARNING TOGETHER
STAY IN THE KNOW
Register for teaching notes, security reading, and new lab updates. We’ll contact you to confirm your subscription.
PLAN YOUR NEXT STEP
Compare credentials for pentesting, networks, cloud, and more. There’s a dedicated route for AI security.
Pick a domain to see a possible route from fundamentals to specialized work.
Build a broad security baseline.
Study ethical hacking methods and terminology.
Prepare for a practical penetration testing exam.
Learn access control, threats, and security operations first.
Use Python to explore AI attacks and defenses.
Assess language models, agents, and AI infrastructure.
Apply AI automation to security engineering and operations.
Learn protocols, routing, and troubleshooting.
Work with network access, IP connectivity, and security basics.
Develop packet analysis and intrusion detection skills.
Understand how systems communicate before securing cloud networks.
Develop a baseline in identity, architecture, and operations.
Explore cloud architecture, data protection, and risk.
These are study suggestions. Check each issuer’s requirements and exam fees. Zsecures offers preparation guidance.
Websites, web applications, APIs, networks, and AI systems can be included in a scoped assessment. Tell us which assets matter most and what you want to learn.
Yes. Depending on the system, we can review prompt injection, unauthorized data access, retrieval boundaries, and what an agent is allowed to do with its tools.
03 / GET IN TOUCH
Tell us a little about the assessment, training, or security project you have in mind. We aim to reply within 24 hours.
Leave out passwords, access tokens, and sensitive assessment details.