
OutBandit
Explore the project source and its README on GitHub.
Open the repository ↗RESEARCH / OPEN SOURCE / LABS
Explore the research behind the lessons, inspect the source code, and try the labs. Much of the learning happens when you take an idea apart yourself.
Read on muzkkir.com ↗THE COMPANION BLOG
Read vulnerability explanations, practical commands, CTF walkthroughs, and security research. The blog is where Muzkkir shares the technical detail behind an investigation.
Explore the blog ↗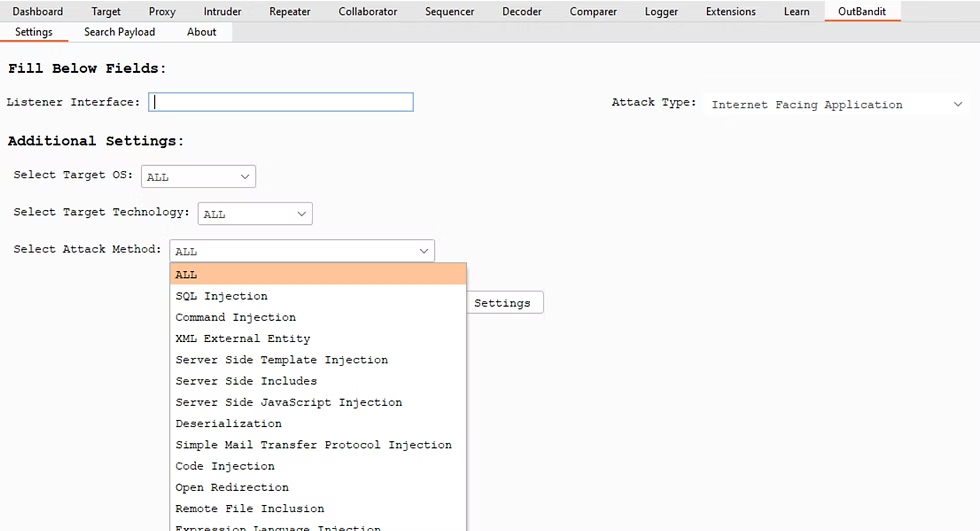
PUBLIC PROJECTS
Explore the project source and its README on GitHub.
Open the repository ↗An offline PDF utility for working with documents locally. Explore the implementation and supported features.
Explore Vellum ↗Find tools, lab projects, and ongoing work in Muzkkir’s public repositories.
Browse GitHub ↗
LABS YOU CAN EXPLORE
CTF LAB
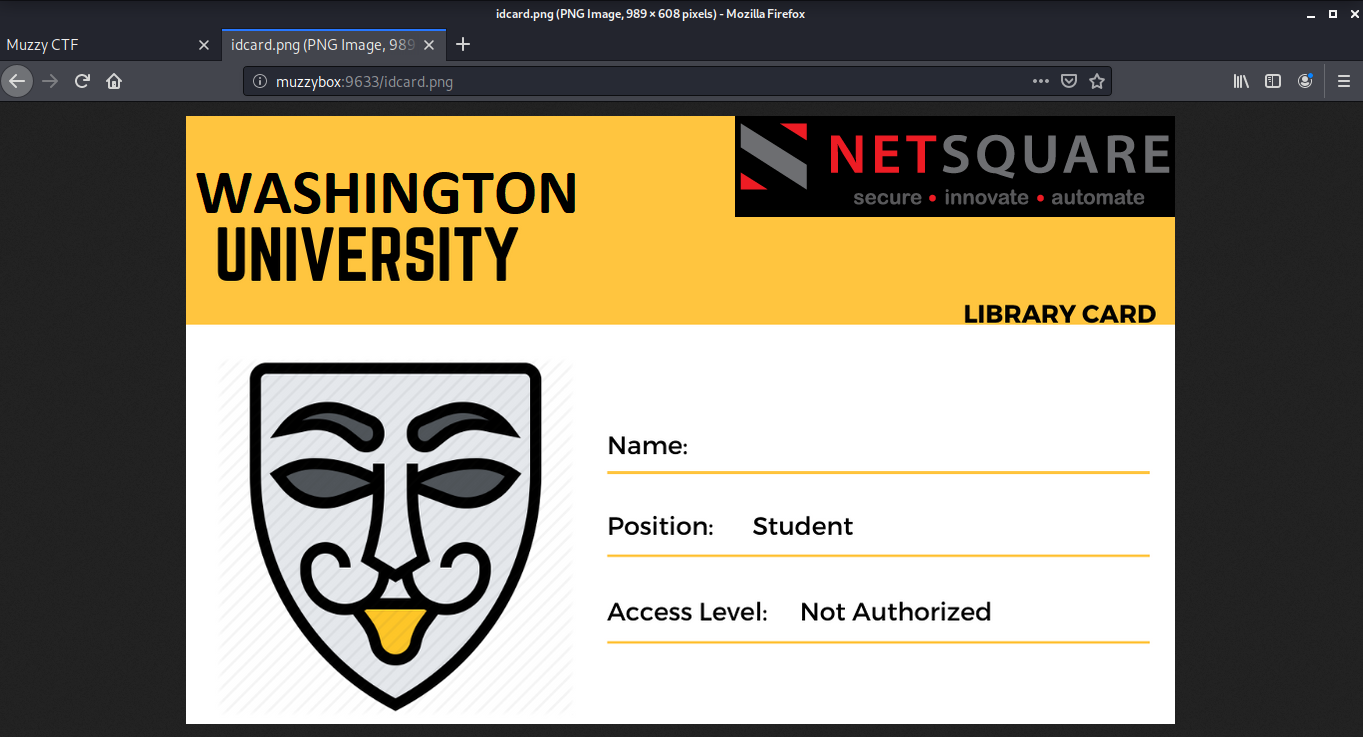
A lab around injection flaws and Linux privilege boundaries, including NoSQL injection and server-side template injection.
COLLABORATIVE LAB
A challenge co-created around HTTP request smuggling, protocol behavior, and socket programming.
STAY CURIOUS
Register for updates about research, projects, and new teaching material.
YOUR NEXT STEP
Explore the four-week crash course, or ask about a focused session for your goals.